Welcome to Your Financial Services Security & Compliance Toolkit
Built for leaders in financial services, this toolkit brings together focused, actionable resources to help you strengthen cybersecurity, streamline compliance, and stay ahead of mounting regulatory expectations.
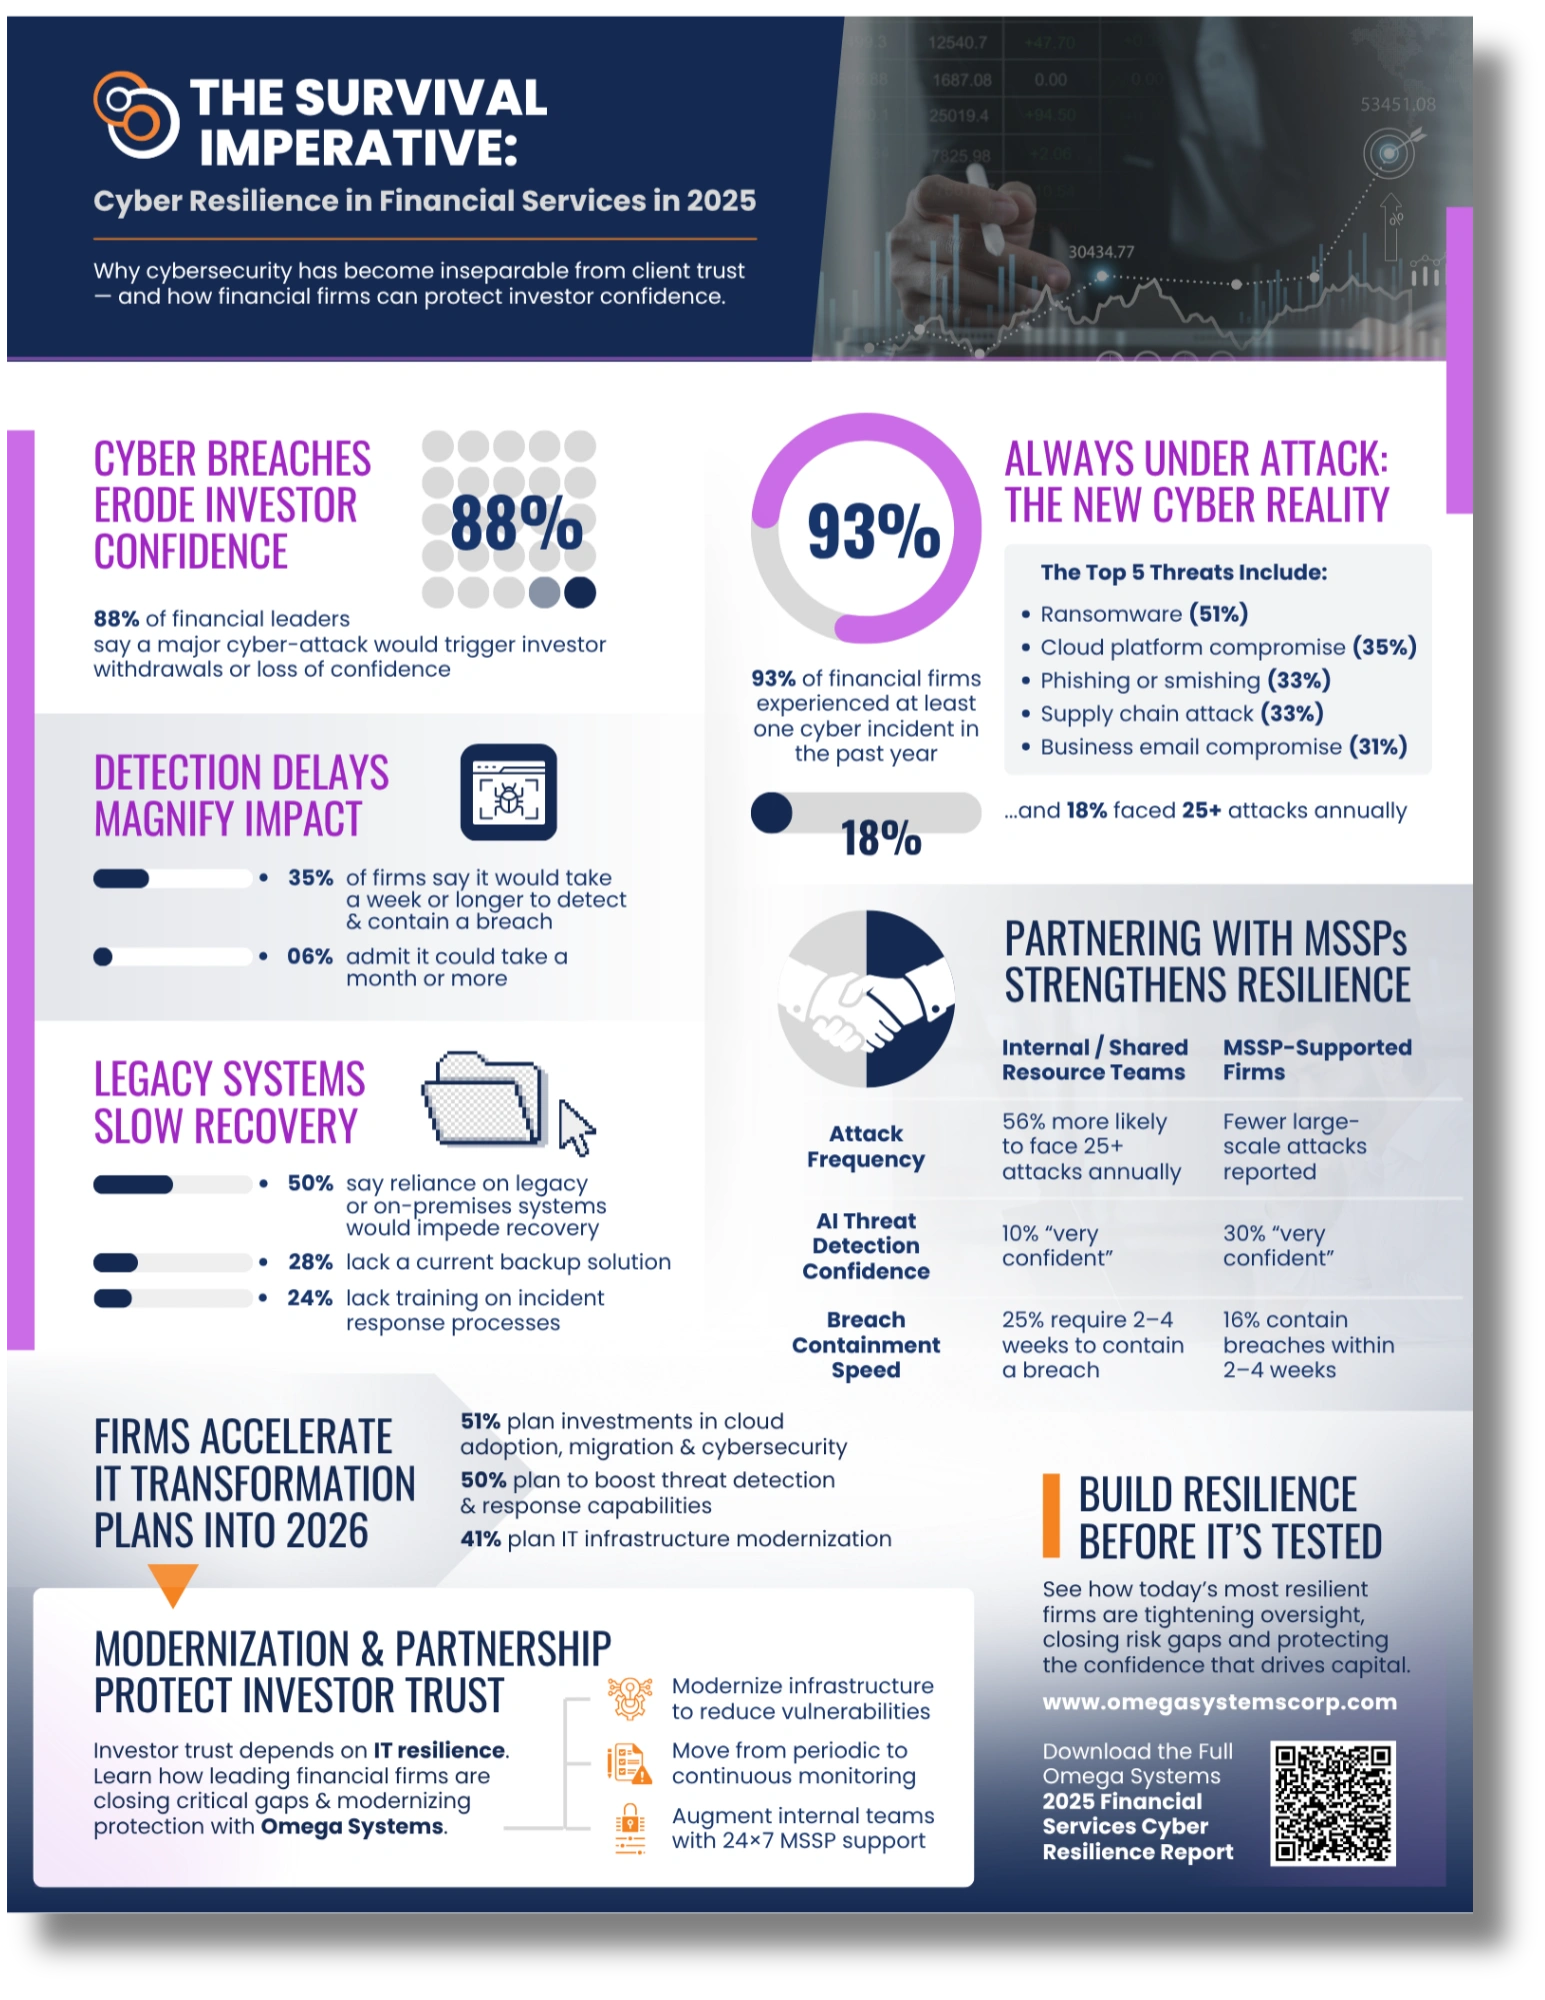
2025 Financial Services Cyber Resilience Report
A data-driven look at how firms are responding to rising cyber threats and operational pressure
Today’s RIAs, private equity firms, hedge funds, family offices, and wealth managers face a perfect storm: aggressive threat actors, expanding attack surfaces, and increasingly complex SEC/FINRA/NYDFS expectations.
This report reveals how firms are adapting — and where costly vulnerabilities remain.
Key insights include:
The true financial impact of cyber incidents
Detection & recovery timelines across the industry
The biggest operational gaps weakening resilience
How investor confidence is tied to cybersecurity readiness
Why firms supported by MSSPs outperform internal-only teams
A sharper, faster look at the regulatory pressure reshaping financial services
This mini report distills the most urgent compliance trends — from documentation gaps to shifting SEC/FINRA/NYDFS expectations — into an easily digestible format your team can act on quickly. Built for fast moving leaders who need clarity without the noise.
Inside the report:
The rise of compliance fatigue across financial services
The top documentation and audit-readiness gaps
How regulatory ambiguity is affecting preparedness
Why manual oversight is putting firms at risk
The case for automation in achieving defensible compliance
Designed for CISOs, compliance leads, COOs, and managing partners who need clarity — fast.
Evaluate how your firm handles documentation, evidence collection, governance, and detection timelines — the six areas where financial firms struggle most.
Start smarter internal discussions
Perfect for CISOs, COOs, and compliance leads who need a quick pulse before exam prep ramps up.
Built around real regulatory pressure
Aligned with SEC, FINRA, and NYDFS expectations to help you gauge if your processes hold up.
Financial services IT is under constant pressure — tighter regulations, smarter attackers, and nonstop digital change. This guide curates the articles top leaders are reading now, offering clear perspectives on cyber risk, compliance readiness, and why managed services are now core to operational resilience. Sharp insights. Zero fluff.
A growing RIA may not need separate IT, cybersecurity, and compliance providers – but it does need clear ownership, the right capabilities, and coordination between them.
How can you tell if your IT provider is truly protecting your financial firm from ransomware, and what should you ask about monitoring, security controls, backup recovery, and incident response?
Investment firms that fail to detect and contain cyber breaches quickly face escalating ransomware costs, regulatory exposure under SEC Regulation S-P, and long-term damage to client trust.
In 2026, financial services firms are reallocating IT budgets toward cybersecurity, compliance automation, cloud modernization, and managed services as resilience and client trust become enterprise imperatives.
As regulators demand faster detection, real-time documentation, and verifiable audit trails, financial firms stuck with spreadsheets and legacy systems are finding that outdated compliance tools have become one of their biggest operational risks in 2026.
Omega Systems’ Financial Services Cyber Resilience Report reveals how U.S. financial firms are confronting rising cyber incidents, fragile investor trust, and the resilience advantage of MSSP partnerships.
From cybersecurity and compliance to uptime and trading execution, hedge funds have unique IT demands. Here are seven critical qualities to look for in a managed services provider (MSP) with financial industry expertise.
For Registered Investment Advisers (RIAs), technology is crucial for operations, compliance & client service. Partnering with a reputable managed IT services provider can simplify IT management, ensuring security, scalability & efficiency.
Financial services IT is under constant pressure — tighter regulations, smarter attackers, and nonstop digital change. This guide curates the articles top leaders are reading now, offering clear perspectives on cyber risk, compliance readiness, and why managed services are now core to operational resilience. Sharp insights. Zero fluff.
Blog
Does Your RIA Need Separate IT, Cybersecurity and Compliance Providers?
A growing RIA may not need separate IT, cybersecurity, and compliance providers – but it does need clear ownership, the right capabilities, and coordination between them.
Omega Systems Names Bill Wosilius CEO to Lead Next Phase of Managed IT and Cybersecurity Growth
Omega Systems has named Bill Wosilius as its new Chief Executive Officer. Wosilius will lead the company’s next phase of growth, building on Omega’s momentum and expanding the value it delivers to organizations operating in complex, highly regulated environments.
How to Tell If Your IT Provider Is Protecting Your Financial Firm from Ransomware
How can you tell if your IT provider is truly protecting your financial firm from ransomware, and what should you ask about monitoring, security controls, backup recovery, and incident response?
Omega Systems Expands Executive Leadership to Support Healthcare & Financial Services Growth
Omega Systems has expanded its executive leadership team with six senior appointments to strengthen managed IT and cybersecurity services for healthcare and financial services organizations.
Why Speed Matters in Financial Services Breach Detection
Investment firms that fail to detect and contain cyber breaches quickly face escalating ransomware costs, regulatory exposure under SEC Regulation S-P, and long-term damage to client trust.
Where Financial Firms Are Spending Their IT Dollars in 2026
In 2026, financial services firms are reallocating IT budgets toward cybersecurity, compliance automation, cloud modernization, and managed services as resilience and client trust become enterprise imperatives.